Set up CMEK with AWS KMS
Create an AWS KMS key, give Anthropic access to it, and put it to use in Claude Platform or Claude Enterprise.
Claude Code
Let Claude Code set up this feature for you
/claude-api help me configure a customer-managed encryption key with AWS KMSIf your Claude Console sidebar shows Account managed by AWS, follow Set up CMEK on Claude Platform on AWS instead.
Before you start
In Claude:
- Customer-managed encryption keys (CMEK) are turned on for your organization.
- You have your Anthropic organization ID, the UUID without the
org_prefix. Copy it from Organization in the Claude Console, or from Organization settings > Organization and access on claude.ai. Whoever creates the key needs it. - You’re an Organization Admin on Claude Platform, or an Owner or Primary Owner on Claude Enterprise.
- On Claude Platform, you have a workspace that retains data, ideally a new one, because existing data stays under Anthropic’s key.
- On Claude Enterprise, you know which features turn off or change.
In AWS:
- You can create AWS KMS keys and set their key policies (
kms:CreateKeyandkms:PutKeyPolicy). - Any IP restriction on AWS KMS access allows Anthropic’s outbound IP addresses.
In AWS: create the key
After a failed Verify or Add, see the fixes for AWS KMS.
Write the key policy
This policy gives Anthropic’s IAM role access to your key. Use only the role ARN published on this page, never one sent by email or chat. Copy the policy into a text editor:
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "AccountRootAdmin",
      "Effect": "Allow",
      "Principal": {
        "AWS": "arn:aws:iam::<AWS_ACCOUNT_ID>:root"
      },
      "Action": "kms:*",
      "Resource": "*"
    },
    {
      "Sid": "AllowAnthropicCMEKCrypto",
      "Effect": "Allow",
      "Principal": {
        "AWS": "arn:aws:iam::915198916910:role/anthropic-cmek-client-us"
      },
      "Action": ["kms:Encrypt", "kms:Decrypt"],
      "Resource": "*",
      "Condition": {
        "StringEquals": {
          "kms:EncryptionContext:anthropic:org_uuid": ["<ORGANIZATION_UUID>"]
        }
      }
    },
    {
      "Sid": "AllowAnthropicCMEKDescribe",
      "Effect": "Allow",
      "Principal": {
        "AWS": "arn:aws:iam::915198916910:role/anthropic-cmek-client-us"
      },
      "Action": "kms:DescribeKey",
      "Resource": "*"
    }
  ]
}
Replace <AWS_ACCOUNT_ID> with your AWS account ID and <ORGANIZATION_UUID> with your Anthropic organization ID. Keep the kms:EncryptionContext:anthropic:org_uuid condition, or verification fails.
You can also limit the key to specific workspaces by listing their compartment IDs. If you’re replacing the policy on a key that already protects Claude data, add one more statement.
Create the key
You can create the key in any AWS commercial region. For the lowest latency, use us-east-2.
To use a key you already have in AWS KMS, replace its key policy.
Open the Create key wizard
Open the AWS KMS console and switch to the region for the key. Go to Customer managed keys and click Create key.
Configure key
Make sure that these options are selected:
- Key type: Symmetric
- Key usage: Encrypt and decrypt
- Advanced options > Key material origin: KMS
- Advanced options > Regionality: Single-Region key
Click Next.
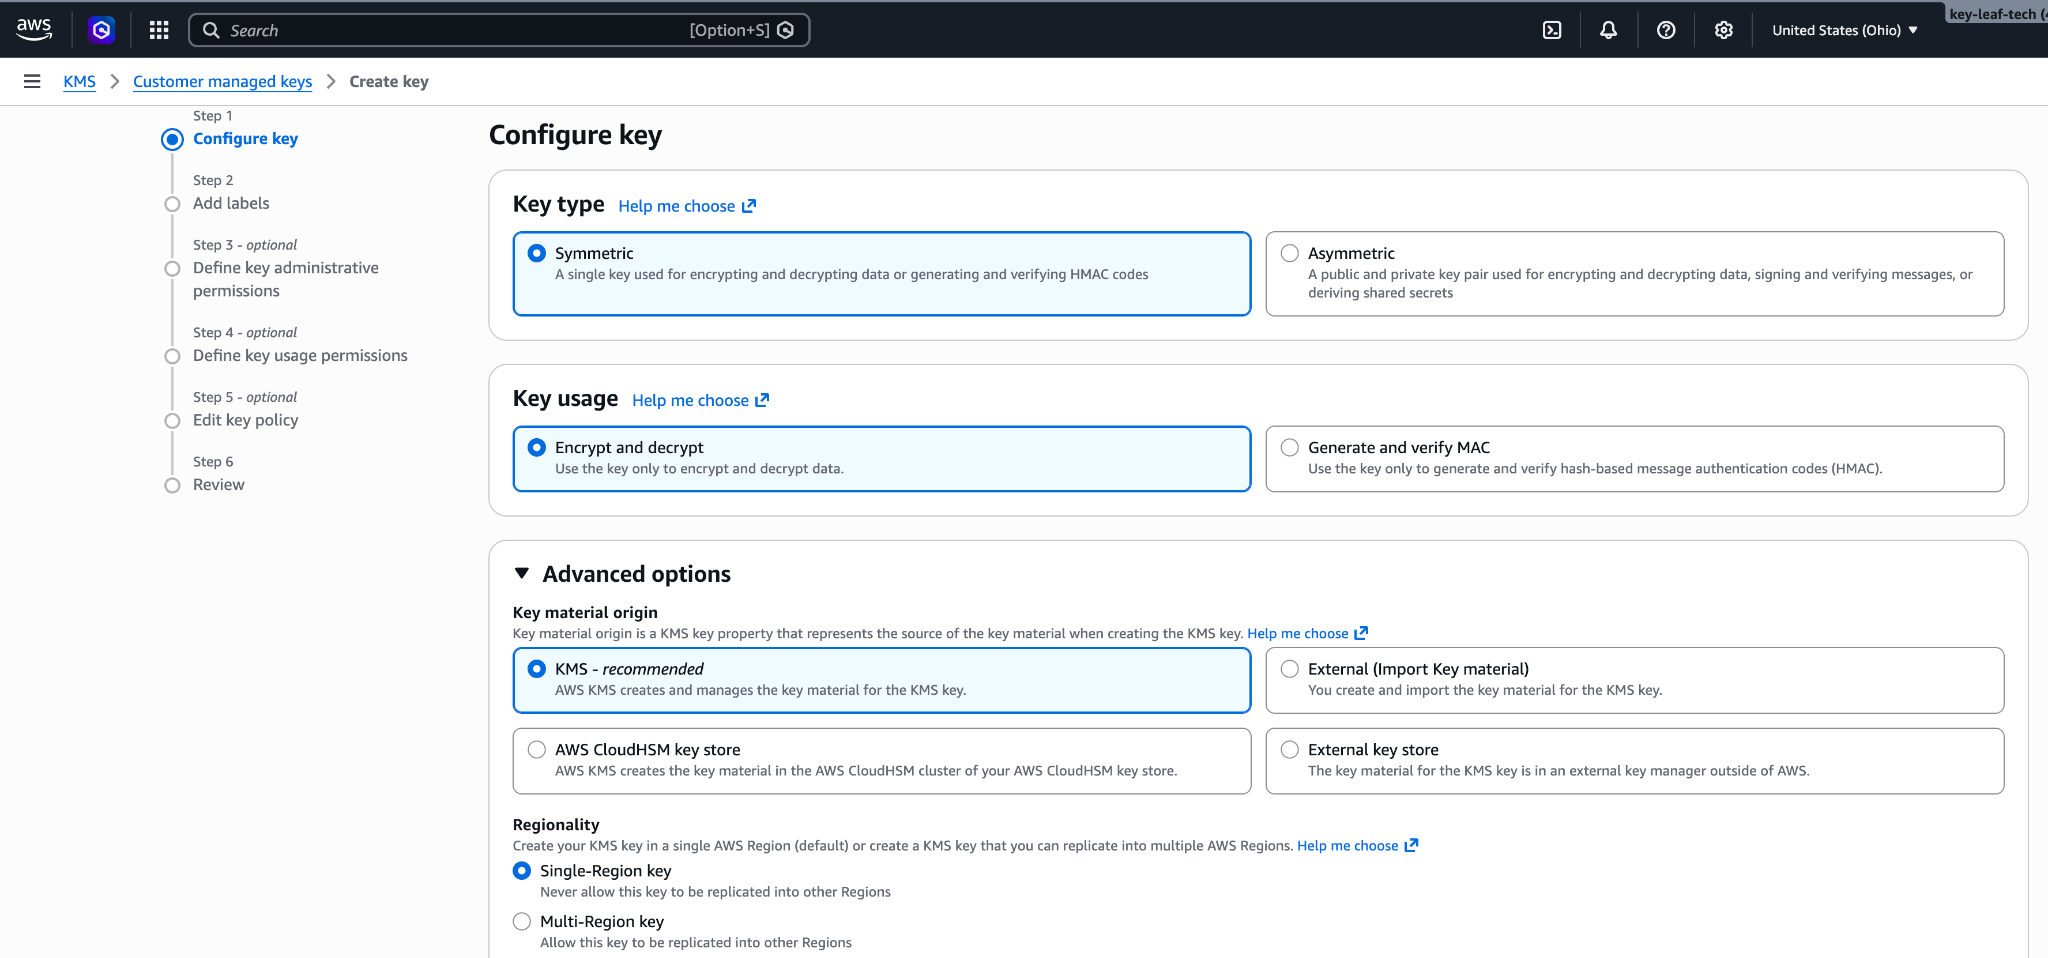
Symmetric, encrypt and decrypt, single-Region key. Add labels
Enter an Alias for the key, such as
anthropic-cmek. Click Next.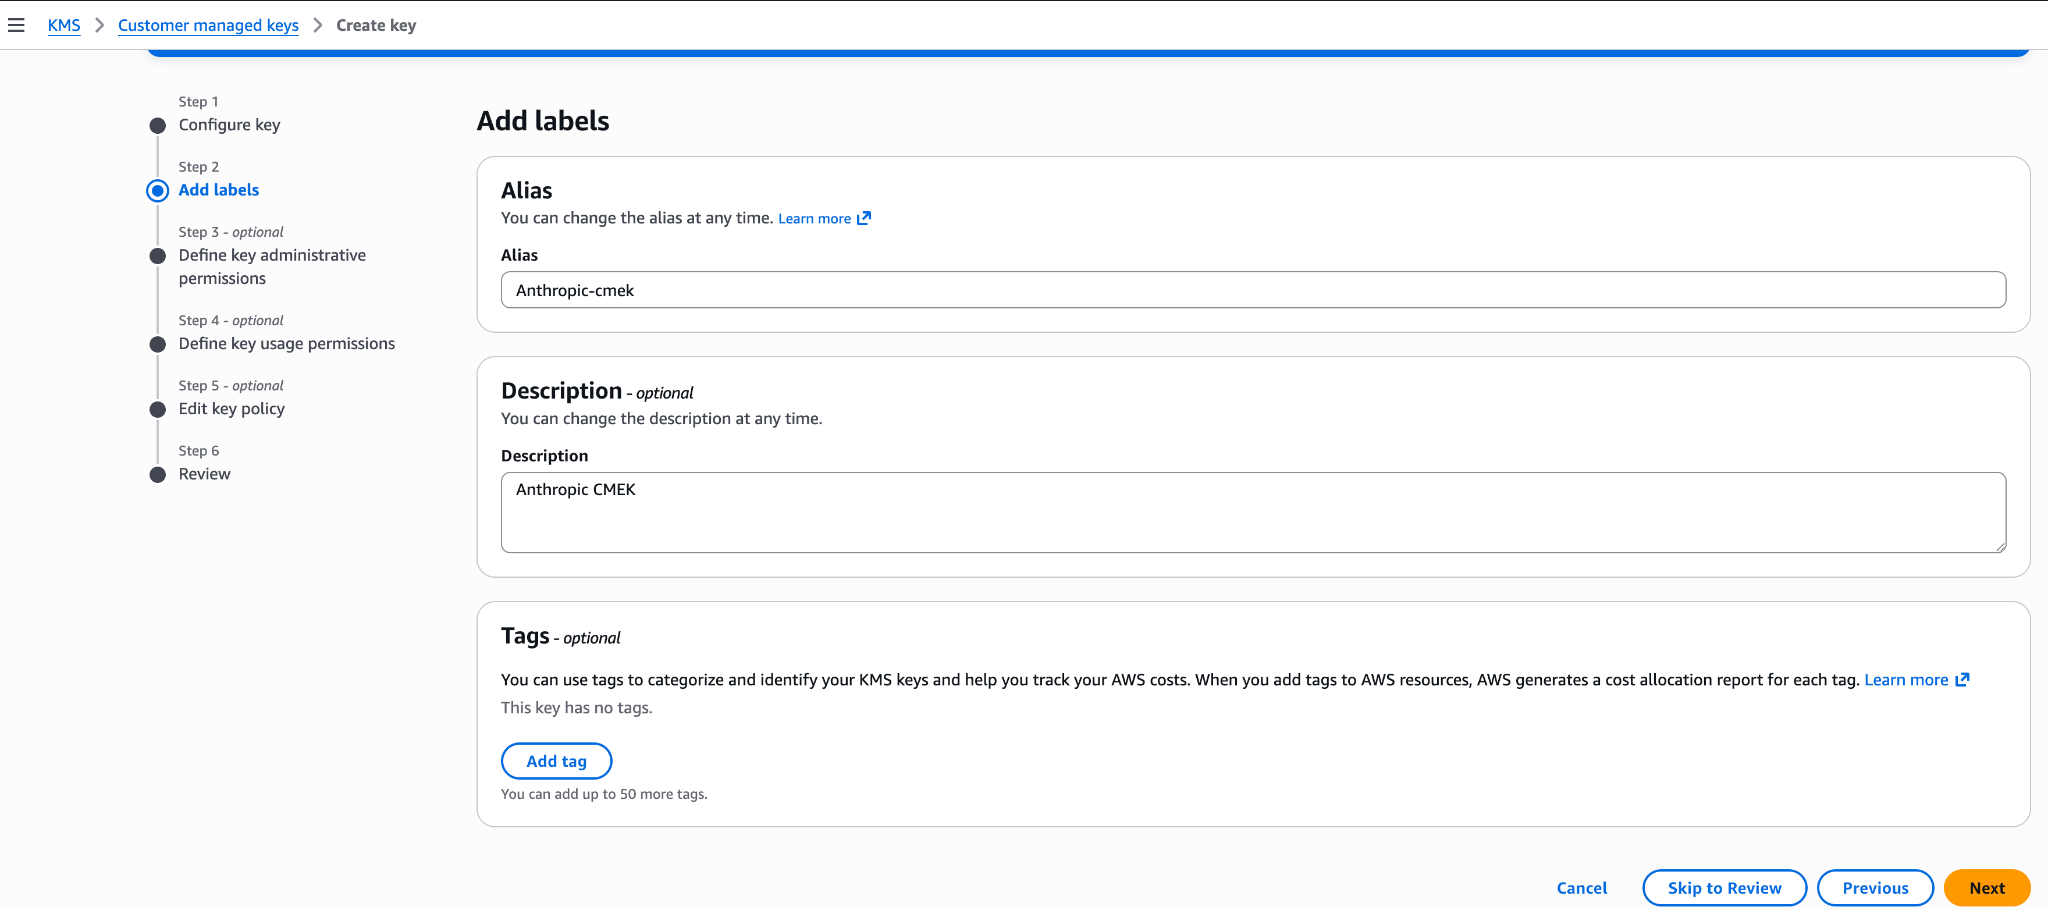
An alias for the key. Define key administrative permissions
Don’t select any key administrators. Your key policy already gives your AWS account full admin control. Click Next.
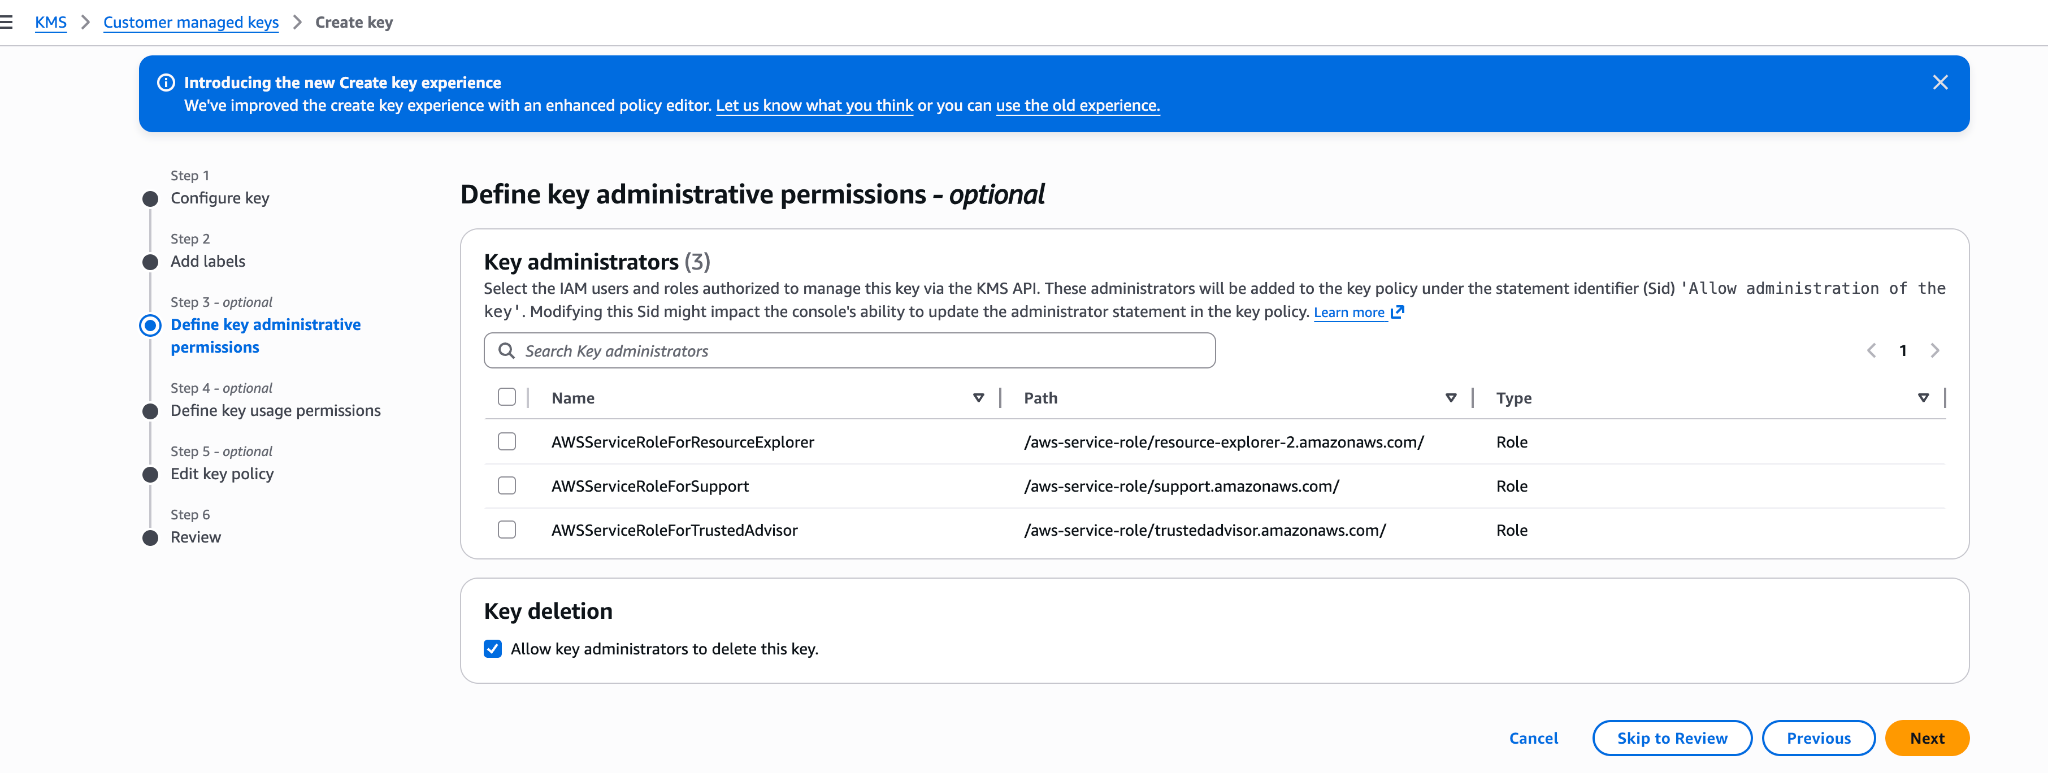
Leave key administrators empty. Define key usage permissions
Don’t select any key users, and don’t add anything under Other AWS accounts. Your key policy already grants the access that’s needed. Click Next.
Edit key policy
Click Edit. Replace the whole policy with your key policy, then click Next.
Review
Click Finish.
Copy the key ARN
In Customer managed keys, open the new key and copy its ARN. Whoever adds the key in Claude needs it.
Save your key policy as key-policy.json, then create the key. Replace <REGION> with the key’s region.
aws kms create-key \
  --region <REGION> \
  --description "Anthropic CMEK" \
  --key-usage ENCRYPT_DECRYPT \
--policy file://key-policy.jsonCopy KeyMetadata.Arn from the output. Whoever adds the key in Claude needs the ARN.
Each check of the key in Claude adds four expected access-denied errors to CloudTrail. You can filter them out.
In Claude: add and attach the key
To script this part on Claude Platform, use the Admin API instead.
Open the encryption key settings
In the Claude Console, open Encryption keys on the Data retention page. If the section isn’t there, select Organization from the dropdown menu at the top.
Add the key
Under Encryption keys, click Add key. Enter a Display name, select AWS KMS, and click Continue.
Enter the key ARN
Check that your key policy contains the Organization ID for the key policy shown in the dialog box. Paste the key ARN into KMS key ARN and click Add.
Verify the key
In the Encryption keys list, click Verify next to the key. Connected appears when the check passes. If Connection failed appears instead, see Troubleshoot CMEK.
Attach the key to a workspace
- At the top of the Data retention page, select the workspace from the dropdown menu.
- Under Encryption key, select the key and click Save.
- Select the checkbox to confirm that you have read the CMEK documentation, then click Confirm.
You see Workspace settings updated. Once the key takes effect, your cloud provider’s audit log shows Anthropic’s calls to the key.
In a ZDR organization, after you select the workspace, select Standard data retention so that Encryption key appears. After you click Save, click Accept on the data retention terms.
On Claude Enterprise, CMEK applies to the whole organization, and you can add only one key.
Adding the key turns off or changes some features for every user. To try CMEK first, use a separate organization.
Open the encryption key settings
Go to claude.ai > Organization settings > Data and privacy and find Encryption keys.
Add the key
Click Add key. Enter a Display name and select AWS KMS. Select the checkbox to confirm that you have read the CMEK documentation, then click Continue.
Enter the key ARN
Check that your key policy contains the Organization ID for the key policy shown in the dialog box. Paste the key ARN into KMS key ARN and click Add.
Confirm that the key was added
The check can take up to 30 seconds. When Encryption key configured. appears, click Done. If The encryption key couldn’t be added. appears instead, find the cause and retry.
Your key protects data written from then on. Tell your users which features changed.
Was this page helpful?